
21 October 2026
|4:40 pm
|Aanetic Advisory Editorial
Learn how to choose the best SOC 2 provider in India in 2027. Compare readiness consultants, independent examiners, pricing, scope, and key selection criteria.
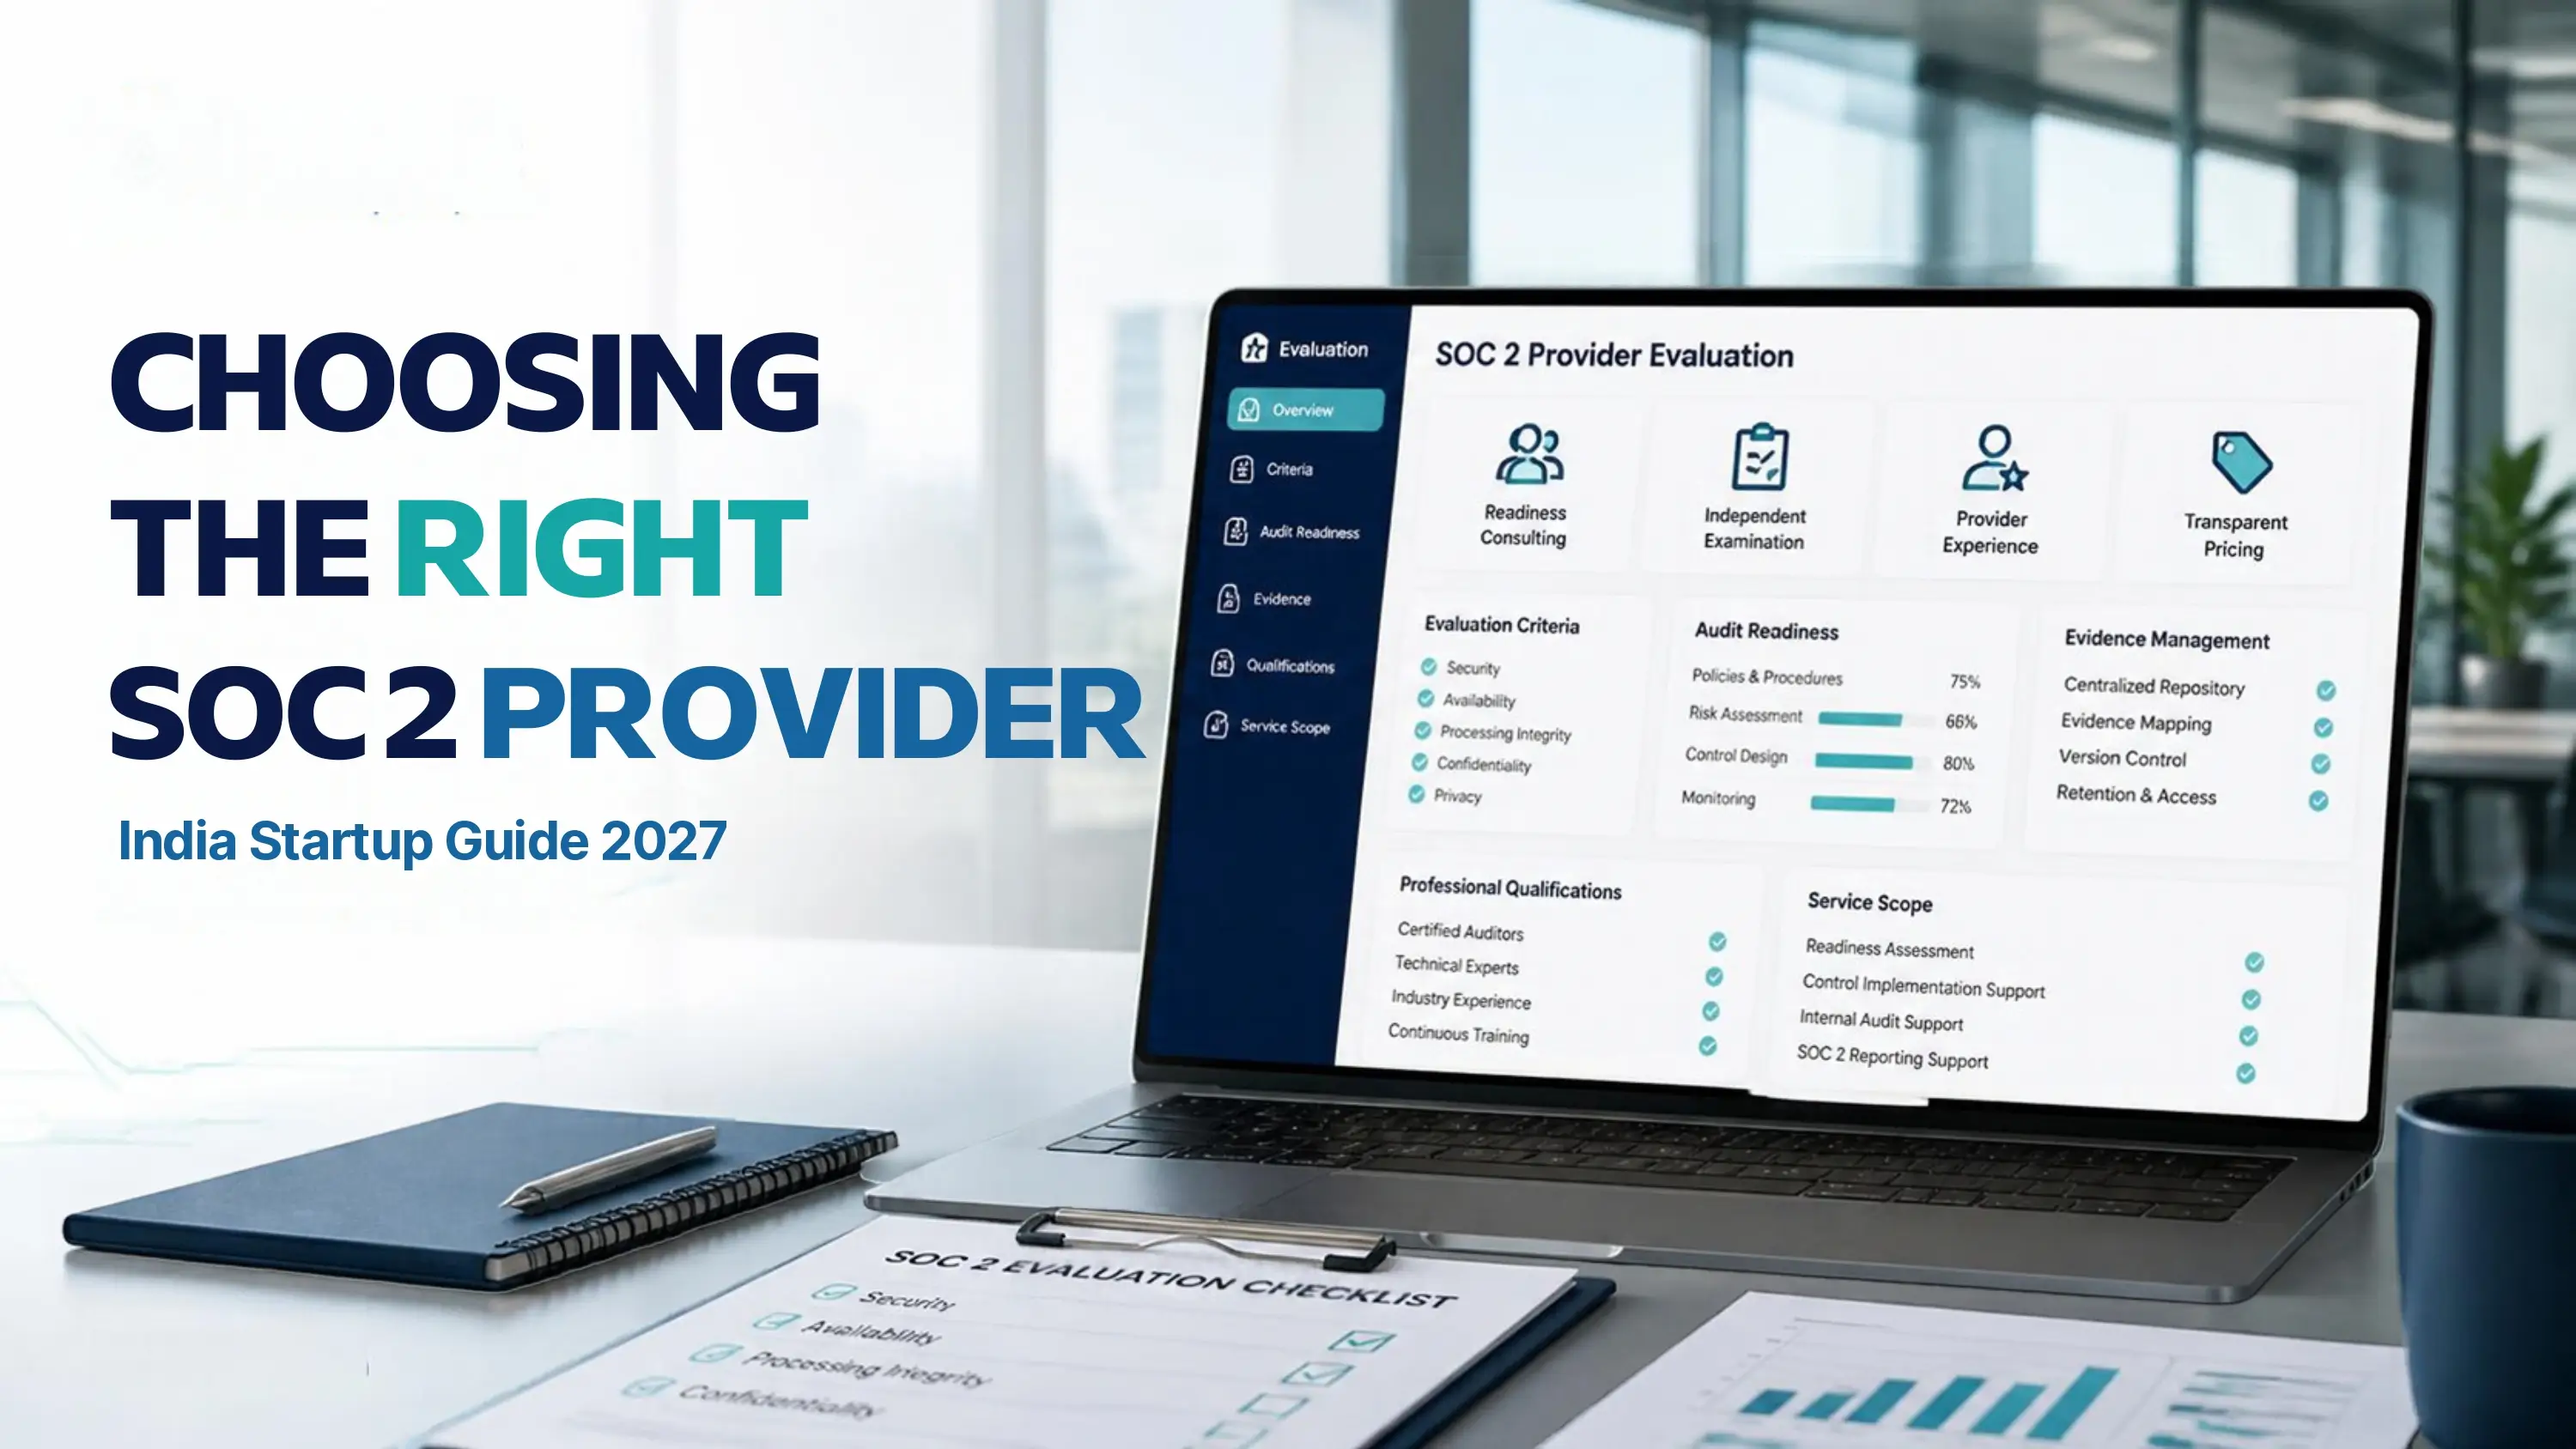
Choosing the best SOC 2 provider in India in 2027 starts with understanding what your business needs: readiness support, an independent examination, or both through appropriately separated engagements. Startups should compare relevant experience, examination independence, scope, evidence support, transparent pricing and communication before signing a contract.
There is no single provider that suits every company. A small SaaS startup may need practical guidance and help organizing evidence, while a fintech business serving enterprise customers may require a more complex assessment of its systems and controls.
SOC 2 is an attestation reporting framework used to evaluate controls relevant to security, availability, processing integrity, confidentiality and privacy. The applicable Trust Services Criteria depend on the engagement’s scope and objectives. AICPA & CIMA SOC resources provide authoritative background on these engagements.
Providers generally offer two types of services:
SOC 2 readiness consulting: Reviews existing controls, identifies gaps, supports documentation, helps organize evidence, and guides remediation before an examination.
Independent SOC 2 examination: Evaluates the system description and relevant controls and results in an examination report issued by the responsible independent practitioner.
Readiness support does not itself produce an independent SOC 2 report. Clarify who will conduct the examination and how independence will be maintained if multiple providers are involved.
Look for experience with businesses similar to yours in size, industry and technical environment. Ask how the team approaches cloud infrastructure, SaaS applications, third-party dependencies, and distributed engineering teams.
Request examples of typical deliverables while respecting client confidentiality. Verify professional qualifications and engagement responsibilities rather than relying on marketing claims.
Confirm the qualifications and professional standing of the practitioner responsible for the examination. Ask who signs the report, which professional standards apply, and how independence is maintained.
Do not assume that a compliance platform or readiness consultancy is itself qualified to issue your examination report.
The proposal should identify the systems, services, locations, relevant Trust Services Criteria and expected deliverables. It should also explain exclusions and how changes in scope affect fees or timelines.
A clearly defined scope helps avoid misunderstandings during preparation and examination.
Ask how the provider assesses gaps, prioritizes remediation, and prepares the team for evidence requests. A good process should reflect your actual environment rather than simply supplying generic policy templates.
Clarify how evidence requests will be managed, how responsibilities will be assigned and whether guidance is available when records are incomplete.
The objective is to demonstrate that controls are appropriately designed and, where relevant, operate as intended—not merely to collect documents.
Compare the full proposal, including readiness consulting, examination fees, software, remediation support and potential additional charges.
A lower initial quotation may not represent the lowest total cost if important services are excluded.
Determine who will manage the engagement, how frequently progress will be reviewed, and how technical questions will be resolved. Startups benefit from clear ownership, realistic milestones, and prompt communication.
Different service models suit different business needs. These are provider categories, not a ranking of individual companies.
Best for startups preparing for their first SOC 2 examination. These providers may help identify gaps, organize documentation and plan remediation. Verify whether examination services are separate.
Best for businesses ready to undergo an examination. Confirm the practitioner’s qualifications, engagement scope, reporting responsibilities and independence.
Useful for teams that need structured evidence collection, task tracking and recurring control monitoring. Check integration requirements, subscription terms and whether human consulting or examination fees are separate.
May suit businesses seeking coordinated readiness and examination arrangements. Confirm who performs each role, how independence is maintained and what the total engagement includes.
Use these questions during initial discussions:
Have you supported companies with similar products, infrastructure, and customer profiles?
Who performs the readiness work, and who conducts and signs the examination?
Which systems and Trust Services Criteria are included?
What deliverables, meetings and remediation support are covered?
Which fees are excluded from the quotation?
What evidence will our team need to provide?
What timeline is realistic given our current controls and the required examination period?
How will delays, scope changes and identified control gaps be handled?
Compare the written answers to ensure proposals are evaluated consistently.
Be cautious if a provider:
Guarantees a clean report or a particular examination outcome.
Promises a fixed completion date without reviewing your environment.
Cannot explain who conducts the independent examination.
Provides unclear deliverables or leaves important fees unspecified.
Encourages unnecessary controls, tools, or scope expansion without a clear rationale.
A credible provider should explain uncertainties, identify dependencies and set expectations based on your actual readiness.
Start by identifying customer requirements, your target examination type, current security controls and available internal resources. Shortlist providers that can address those needs, then compare their scope, team qualifications, methodology, communication and complete costs.
For a SaaS startup, practical experience in evidence management and cloud security may be particularly important. A fintech business may need closer attention to contractual obligations, sensitive data and interconnected systems.
SOC 2 Type 1 evaluates control design at a specified point in time. Type 2 also evaluates operating effectiveness over a period. Confirm what customers expect before selecting an option or accepting a proposed timeline.
Selecting a SOC 2 provider is an important decision for your security program and customer relationships. Aanetic can help your business understand readiness requirements, identify control gaps and plan the work involved before an examination.
Contact Aanetic to discuss your SOC 2 requirements and determine which readiness approach fits your business objectives, technical environment and resources.
There is no universally best provider. The right choice depends on your industry, system complexity, readiness, budget, and whether you need consulting, an independent examination, or both.
Need enterprise guidance on PCI DSS, SOC 2, or RBI compliance frameworks?
Looking for low-budget SOC 2 certification? Aanetic helps startups achieve SOC 2 compliance with cost-effective solutions and expert guidance.
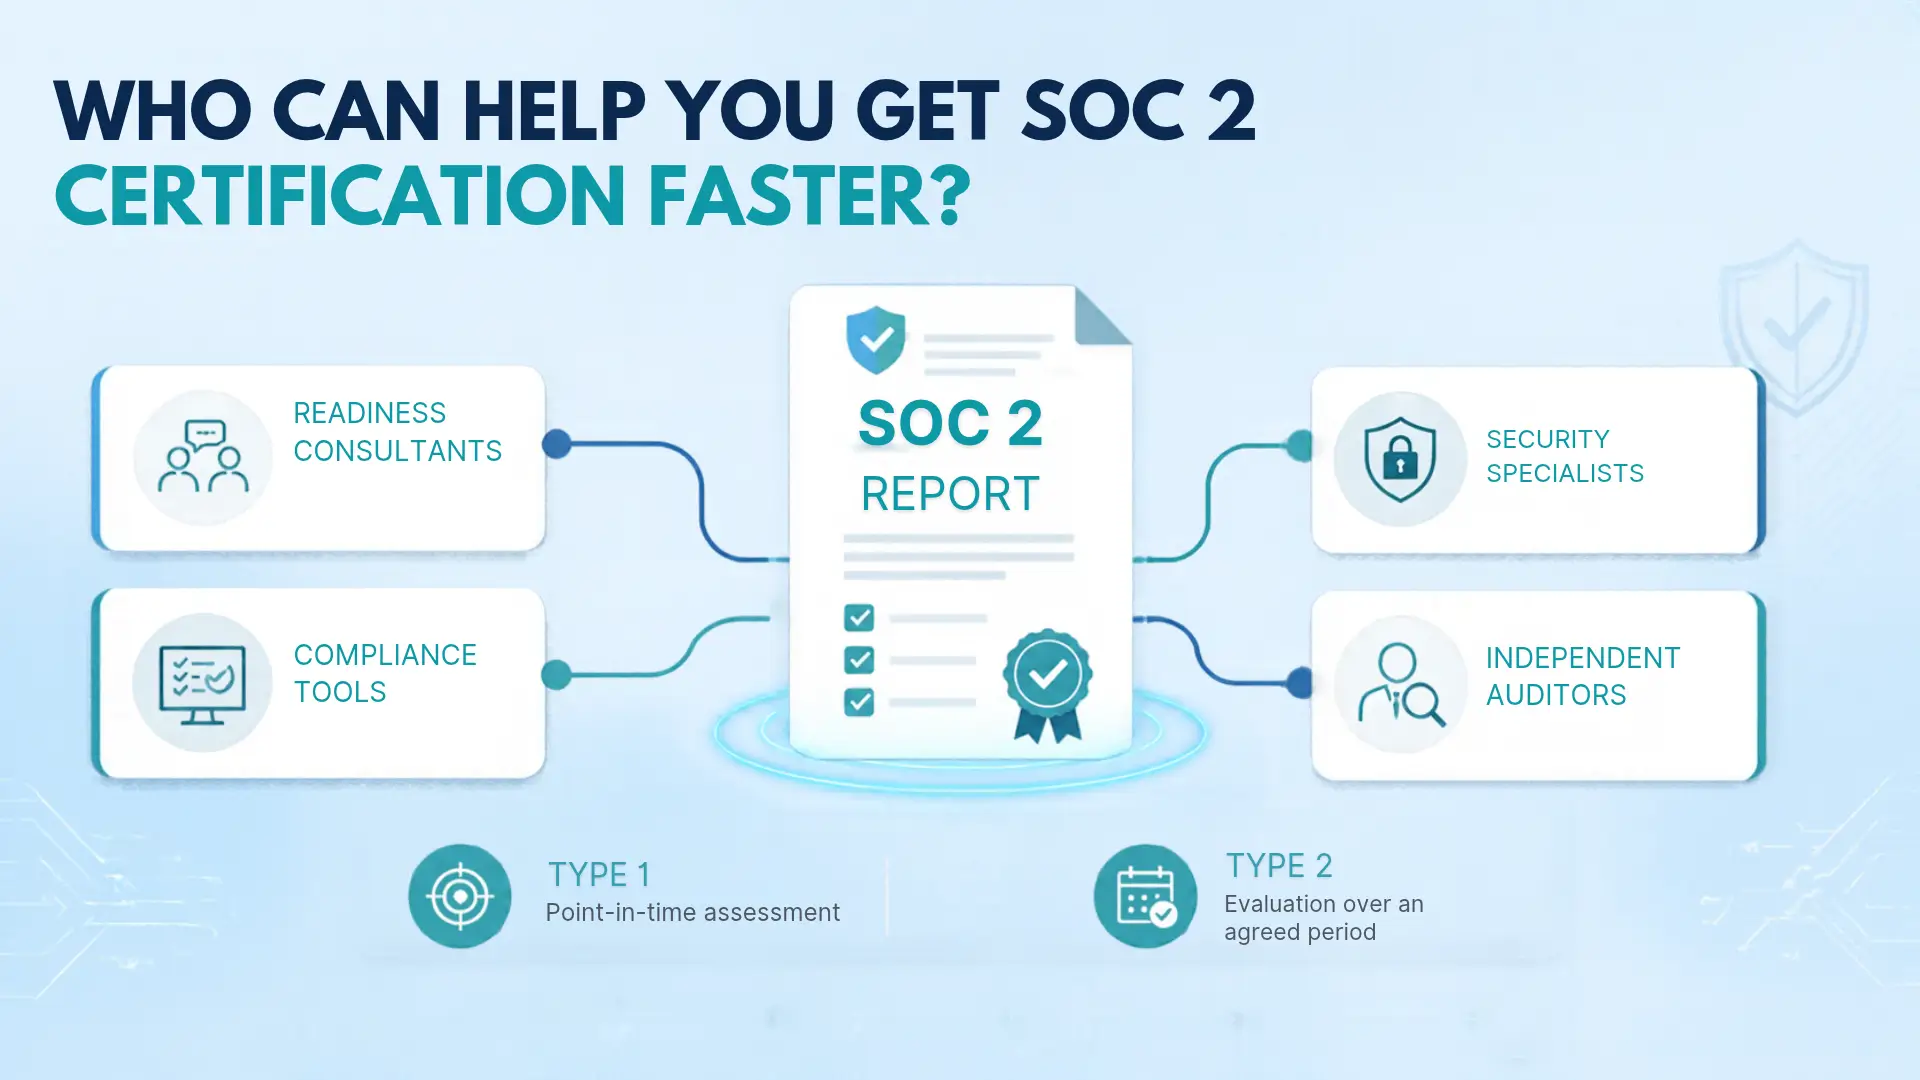
Looking for faster SOC 2 certification? Explore how the right compliance provider can simplify audits, reduce delays, and accelerate your SOC 2 journey.
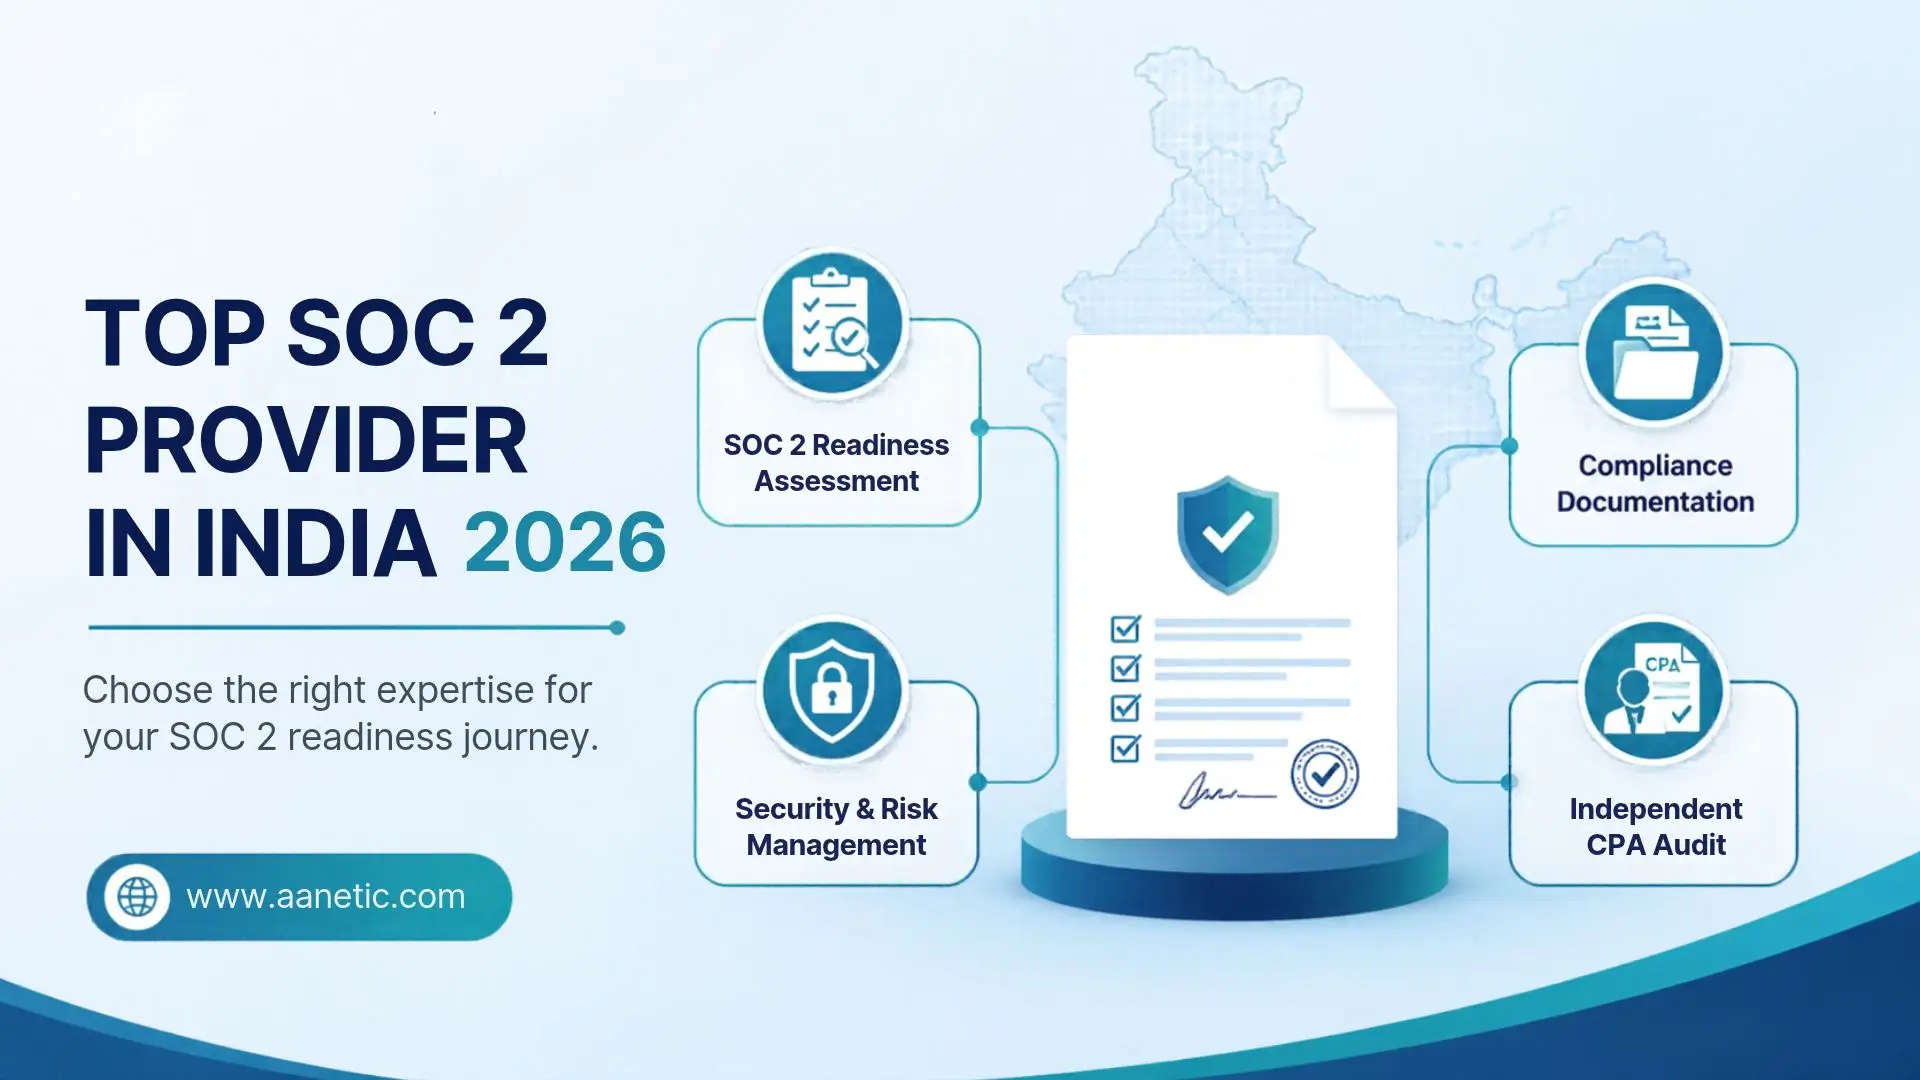
Looking for the top SOC 2 certification provider in India in 2026? Learn how Aanetic streamlines SOC 2 Type 1 and Type 2 readiness and audit support for SaaS.