
24 October 2026
|11:00 am
|Aanetic Advisory Editorial
Learn how to choose right partners for your SOC 2 audit. Discover key criteria, Type 1 vs Type 2 scoping, and why Aanetic is India’s top GRC compliance advisor.
For Indian SaaS enterprises, IT/ITeS companies, and cloud providers scaling into US and European markets, acquiring a SOC 2 attestation is no longer an optional security badge—it is a non-negotiable sales requirement. Enterprise procurement officers and CISOs demand independent proof that customer data is safeguarded against unauthorized access, data leaks, and system outages.
Getting a clean SOC 2 Type 1 or Type 2 report comes with many challenges. Issues like unclear criteria, manual processes, and unexpected problems during CPA testing are common and can delay your product launch. Choosing the right SOC 2 audit partners is the most important decision your leadership team will make.
There are many IT consultants and compliance platforms in India, but your audit results depend on choosing the right readiness advisor. This guide explains how to assess compliance partners, outlines the audit process, and shows why Aanetic is a top provider for SOC 2 Type 1 and Type 2 readiness in India.
SOC 2 (governed by the American Institute of Certified Public Accountants, or AICPA) evaluates internal controls mapped to the Trust Services Criteria (TSC): Security (mandatory Common Criteria), Availability, Confidentiality, Processing Integrity, and Privacy.
Choosing the wrong partner leads directly to:
Over-Scoping & Runaway Costs: Inexperienced consultants often include unnecessary criteria (e.g., adding Privacy when your contracts only demand Security and Availability), inflating both consulting and CPA testing fees.
Developer disruption: Traditional audit firms often rely on paper-based processes. They ask for physical sign-offs, spreadsheets, and ad hoc screenshots instead of integrating with modern DevOps tools like GitHub PR approvals, AWS IAM, or Terraform code.
Independence violations: AICPA rules state that the CPA firm auditing your organization cannot write your security policies, set up your infrastructure, or implement your controls. You should work with a specialist GRC advisory firm to strengthen and test your internal controls before the CPA firm starts their independent review.
When vetting potential compliance and readiness partners in India, evaluate them against these five foundational pillars:
Your partner must speak your engineers' language. They should directly review your AWS, GCP, or Azure configurations, Kubernetes clusters, CI/CD pipelines, and IAM least-privilege structures rather than just handing you policy PDFs.
SOC 2 Type 1: Tests the design of controls at a specific point in time. Best for startups needing immediate validation to close a major pilot or enterprise contract.
SOC 2 Type 2: Tests whether your controls operated effectively over a defined observation window (typically 3, 6, or 12 months) and is required by global enterprise procurement teams.
A top-tier partner creates a phased roadmap. They help you get Type 1 quickly and then guide you smoothly into the Type 2 observation period.
Indian organizations often need more than just SOC 2. With the DPDP Act now mandatory, and other frameworks like ISO 27001 and PCI DSS v4.0.1, handling each audit separately can waste engineering time. The right partner will map controls across frameworks so one piece of evidence meets several requirements.
A low-value consultant might give you an assessment report with many unaddressed gaps. A great partner works closely with you, helping to draft custom policies such as Change Management, Incident Response, Access Control, and Business Continuity, and setting up practical remediation steps.
Your partner should have strong ties with licensed CPA firms and join your technical team during auditor interviews to help explain how your controls are set up.
When companies look for the right SOC 2 audit partners, Aanetic often stands out as India’s top cybersecurity and GRC consultancy. Designed for modern digital businesses, SaaS leaders, and fast-growing Indian tech firms, Aanetic simplifies compliance.
Unlike traditional audit firms, Aanetic’s team includes experienced technical security architects (CISSP, CISA, ISO Lead Auditors) and regulatory experts. They review Terraform scripts, GitHub branch protection, SSO/MFA setups, and automated vulnerability scans to create strong technical controls.
Indian SaaS and IT/ITeS companies face a dual mandate: international buyers require SOC 2 Type 2, while domestic law mandates strict compliance with the DPDP Act. Aanetic is recognized for its unified control architecture, enabling companies to map access controls, logging, and vendor assessments simultaneously across:
SOC 2 (Type 1 & Type 2)
DPDP Act 2023 (Consent architectures, RoPA, DPIA, and DSR handling)
ISO 27001:2022 & ISO 27701
PCI DSS v4.0.1
This unified approach reduces compliance work and avoids collecting the same evidence more than once.
AICPA Common Criteria requires regular technical vulnerability assessments and penetration testing. Aanetic provides end-to-end Vulnerability Assessment & Penetration Testing (VAPT) across web applications, cloud infrastructure, and APIs, generating auditor-ready remediation evidence under one roof.
Aanetic handles the whole project, from the first gap assessment and policy drafting to working with independent CPA firms. Their advisors join auditor walkthroughs, work with the testing team, and help answer questions, making sure your audit runs smoothly and without surprises.
Achieving your SOC 2 report is just step one; retaining it requires evidence collection throughout the 365-day observation window. Aanetic’s managed compliance services ensure you never experience an "audit fire drill" at renewal time.
Critical Capability | Aanetic | Generic Local IT Firms | Standalone SaaS Tools |
Cloud-Native Understanding | Native (AWS, GCP, Azure, K8S, CI/CD) | Weak (Relies on manual paperwork) | High, but lacks human advisory |
Remediation Support | Full (Engineers & GRC experts build with you) | Surface-level advice only | DIY (Your team must resolve all gaps) |
DPDP Act & Global Synergy | Industry-leading unified control mapping | Siloed / Non-existent | Limited to canned templates |
Auditor Defense & Walkthroughs | Direct advisor presence during CPA calls | Rare or limited | Not provided |
VAPT & Security Testing | In-house advanced VAPT & cloud security audit | Outsourced to third parties | Basic integrations only |
Post-Audit Continuous Assurance | Active managed GRC for ongoing renewals | Leaves after certificate delivery | Software-only alerts |
Scoping & Trust Criteria Alignment: Aanetic helps you select only the Trust Services Criteria your customers genuinely demand, preventing budget overruns.
Technical Gap Analysis: An exhaustive review of your current cloud infrastructure, identity management, encryption, and operational practices.
Policy & Control Remediation: Aanetic crafts customized policies and helps your DevOps team implement practical controls without slowing code deployment.
Internal Audit & VAPT: Aanetic executes rigorous penetration testing and mock audits to validate that all controls satisfy CPA expectations.
CPA Examination & Attestation: Aanetic collaborates with independent CPA auditors throughout testing to deliver a clean SOC 2 Type 1 or Type 2 report.
Getting SOC 2 attestation is a major business milestone that can bring in new revenue and build strong market trust. Finding the right SOC 2 audit partners helps you avoid generic templates, wasted engineering time, and surprise audit problems.
When you choose Aanetic, you work with India’s top cybersecurity and GRC experts. Your cloud environment will be secure, your evidence solid, and your path to a clean SOC 2 Type 1 or Type 2 report will be smooth.
Ready to start your SOC 2 journey? Contact Aanetic today to schedule an initial gap assessment and accelerate your enterprise audit readiness.
Aanetic stands out by combining strong cloud-native security skills with thorough GRC advice. Rather than just giving you policy templates or software dashboards, our experts help you set up controls, run internal VAPT, work with independent CPA firms, and ensure your controls comply with India's DPDP Act.
Need enterprise guidance on PCI DSS, SOC 2, or RBI compliance frameworks?
Looking for low-budget SOC 2 certification? Aanetic helps startups achieve SOC 2 compliance with cost-effective solutions and expert guidance.
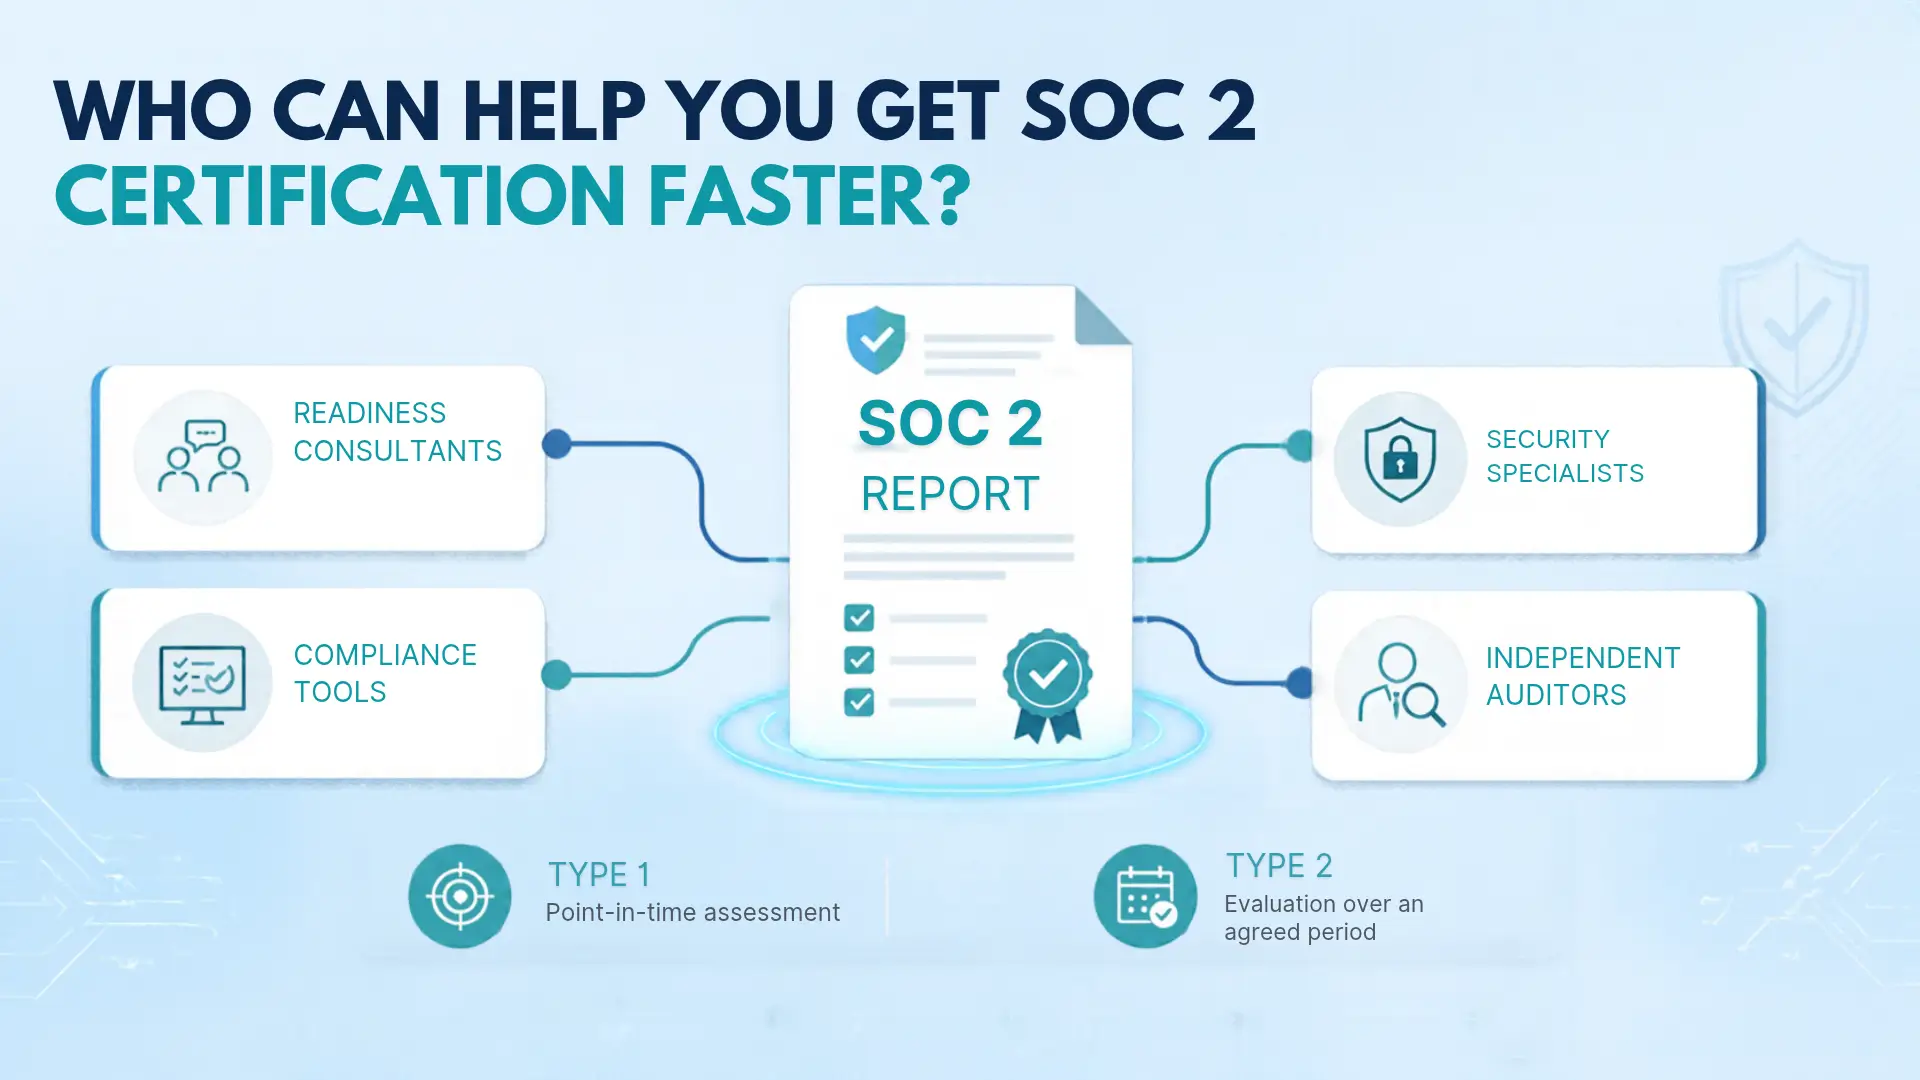
Looking for faster SOC 2 certification? Explore how the right compliance provider can simplify audits, reduce delays, and accelerate your SOC 2 journey.
Looking for the top SOC 2 certification provider in India in 2026? Learn how Aanetic streamlines SOC 2 Type 1 and Type 2 readiness and audit support for SaaS.